
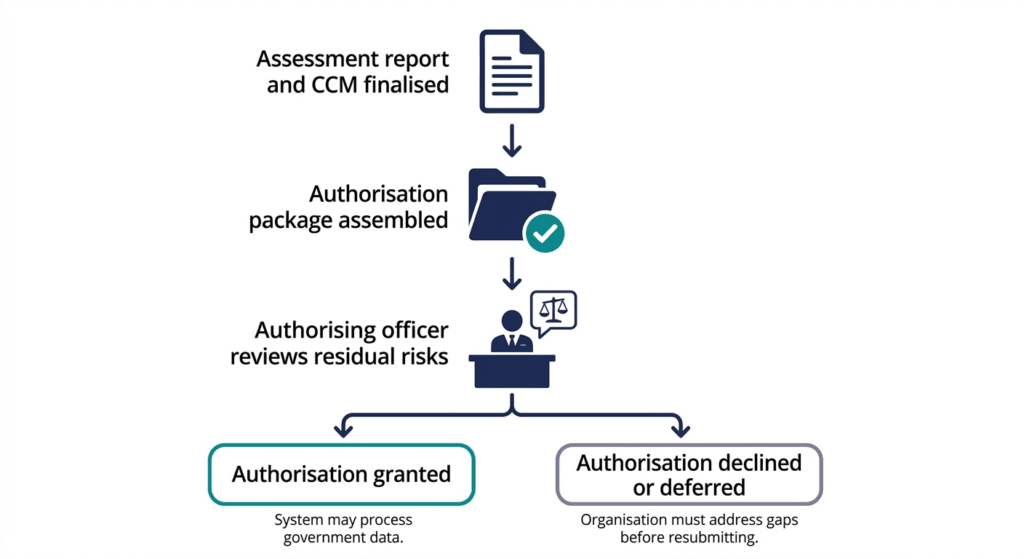
The authorisation package is the set of documents an authorising officer uses to decide whether to approve a system to operate. The IRAP assessment report is central, not the whole package. The officer weighs the residual risks against the organisation’s risk appetite before authorising, and a completed assessment does not guarantee the decision goes the applicant’s way.
The authorisation package is the suite of documents provided to the authorising officer so they can make a risk based decision about whether to approve the system for operation. The IRAP assessment report is a central component, but it is not the whole package. The authorising officer reviews the package, weighs the residual risks against their organisation’s risk appetite, and makes the authorisation decision. A completed IRAP assessment does not guarantee that decision will go in the system’s favour.
By the time the finalised IRAP assessment report and the cloud controls matrix are in hand, the findings are understood. A typical position is two controls remediated before the package is submitted, one finding open with a documented business constraint, and three recommendations acknowledged and scheduled for a future uplift cycle. The next task is assembling everything the agency’s authorising officer needs to make their decision, and this is not simply a matter of forwarding the report.
What goes in the IRAP authorisation package?
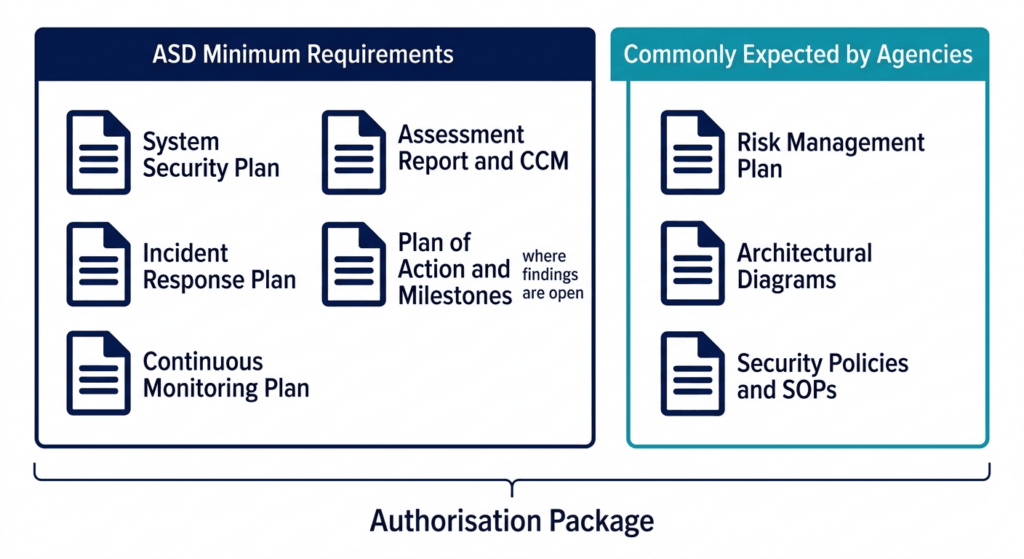
The authorisation package is the complete set of documents submitted to the authorising officer. The IRAP assessment report and the cloud controls matrix are central to it, but the IRAP Consumer Guide specifies a wider minimum set of artefacts.
| Document | What it is | When it is required |
|---|---|---|
| System Security Plan (the SSP-A for cloud systems) | Describes the system, its architecture, its data flows and the controls in place; it must reflect the system as it is at authorisation, not as it was when the assessment began | Always |
| Cyber security incident response plan | How the organisation detects, responds to and recovers from an incident affecting the system | Always |
| Continuous monitoring plan | What is monitored, how often, and what triggers a review or reassessment after authorisation | Always |
| IRAP assessment report and cloud controls matrix | The narrative picture of the security posture, plus the control by control detail | Always |
| Plan of action and milestones (POAM) | Open findings, planned remediation, ownership and target completion dates | Where material findings remain open |
| Risk management plan, design and architectural diagrams, security policies | Supporting material agencies frequently want to review beyond the ASD minimum | Commonly expected; confirm with the agency |
These are the minimum documents. In practice, authorising officers commonly expect additional supporting material beyond this set. The Consumer Guide’s preparation guidance identifies documents agencies frequently want access to when reviewing a package, including a risk management plan covering the system’s identified risks and treatment decisions, design and architectural documents sufficient to understand how the system is built and how data flows through it, and organisational security policies and standard operating procedures relevant to the system’s operation.
The specific requirements of the consuming agency’s authorising officer should be confirmed before the package is submitted. Some agencies have internal templates or submission requirements that go beyond the ASD minimum. Finding that out after the package is assembled wastes time on both sides. Confirm the agency’s expectations before assembly begins. A common package includes the minimum artefacts plus the risk management plan and architectural diagrams, with the POAM added because findings remain open. Submitting without the POAM leaves the authorising officer with questions that have no formal answers.
Who is the authorising officer in the IRAP process?
For OFFICIAL: Sensitive and PROTECTED outsourced IT systems and cloud services, the authorising officer is the Accountable Authority or Chief Information Security Officer of the entity that owns the system, or their delegate. For a Commonwealth agency consuming a cloud service, that is typically the agency’s CISO, acting as the delegate of the agency’s accountable authority.
The authorising officer is responsible for authorising the system to operate based on acceptance of the residual security risks. That acceptance must happen before the system processes, stores, or communicates government information or data. The PSPF is explicit on this. Operating the system before authorisation is granted is not a grey area. The authorising officer does not assess the system. They review the assessment package, consider the residual risks in the context of their organisation’s objectives, culture and risk tolerance, and make a decision.
What does the authorising officer weigh up in an IRAP authorisation?
The authorisation decision is a risk based judgement, not a pass or fail test. A system with findings can be authorised. A system with no findings can still be declined if the authorising officer has concerns the assessment did not address. The framework gives the authorising officer discretion, which means the quality of the package and the organisation’s ability to explain the residual risks in plain terms both matter.
The authorising officer looks at the gap between what the assessment found and what the organisation has done or committed to do about it. They consider whether the continuous monitoring plan gives them reasonable ongoing assurance. They assess whether the incident response capability is credible. They review the plan of action and milestones for realistic timelines and clear ownership. A POAM that lists every finding as resolved within thirty days, with the system owner as the responsible party for all of them, will not inspire confidence. The authorising officer seeks a balance between system functionality and residual risk. They are not looking for a perfect system. They are looking for a system they can authorise with a clear picture of the risks they are accepting and the controls they are relying on.
Can the authorising officer authorise only part of the IRAP assessed system?
The system authorisation boundary may match the assessment boundary exactly, or it may be a subset of it. An authorising officer can choose to authorise a portion of what was assessed. The authorisation boundary cannot be larger than the assessment boundary. The agency cannot authorise components that were not assessed.
In practice an agency might authorise the production environment and the identity provider configuration while noting the pre-production environment, though assessed, as out of the authorisation boundary, with the expectation that it will not process real government data until a separate authorisation decision is made.
What does IRAP authorisation actually mean?
Authorisation is the formal decision by the authorising officer to accept the residual security risks associated with the system and permit it to operate. It is not a declaration that the system is secure. It is not an endorsement by ASD or the Australian Government. It is the agency taking accountability for the risk decision. This is the same point made in what an IRAP assessment is, and is not: IRAP is an assessment, not a certification, and there is no pass mark.
For a provider, the authorisation letter from the agency’s CISO is the commercial trigger that allows the platform to go live for government data processing. Without it, the platform cannot be used for that purpose regardless of how complete the assessment was. The authorisation is point in time. If the system changes materially after authorisation, the organisation has an obligation to consider whether the existing authorisation still holds, and whether reassessment or a new authorisation decision is required. Cybernion runs independent IRAP assessments and readiness that take this through to a package an authorising officer can act on.
Related reading: IRAP POAM and risk management, understanding the IRAP report and cloud controls matrix, and the complete IRAP assessment guide.
Frequently asked questions
What documents must be in the IRAP authorisation package?
The ASD minimum set is the system security plan, the cyber security incident response plan, the continuous monitoring plan, the IRAP assessment report, the cloud controls matrix, and a plan of action and milestones where findings remain open. In practice, authorising officers frequently expect additional material including a risk management plan, architectural diagrams, and relevant security policies. Confirm the specific requirements with the consuming agency before assembling the package.
Who is the IRAP authorising officer for an OFFICIAL: Sensitive cloud service?
For OFFICIAL: Sensitive and PROTECTED outsourced IT and cloud services, the authorising officer is the Accountable Authority or CISO of the entity that owns the system, or their delegate. For government agencies this is typically the agency CISO acting under delegation.
Does a completed IRAP assessment mean our system will be authorised?
No. The assessment gives the authorising officer the information to make the decision. Agencies have declined to authorise systems that have completed IRAP assessments. The decision rests entirely with the authorising officer, based on their risk appetite and the content of the full package.
What is the POAM and does it need to be in the IRAP authorisation package?
The plan of action and milestones documents open findings from the assessment, planned remediation activities, ownership, and target dates. Its inclusion is expected where material findings remain unresolved. It gives the authorising officer visibility of how and when the organisation intends to address the gaps they are being asked to accept.
Can the authorising officer authorise part of the IRAP assessed system?
Yes. The authorisation boundary may be smaller than the assessment boundary. An authorising officer can authorise specific services or environments that were assessed and exclude others. The authorisation boundary cannot exceed the assessment boundary.
Written by Gaurav Vikash, an ASD endorsed IRAP assessor and senior cyber security leader with 18 years of experience across Australia, the UK and Asia, including CISO and senior security leadership roles. He holds CISSP, CISA, CISM and CRISC and is an ISO 27001 Lead Auditor and ISO 42001 Lead Implementer, and speaks regularly at industry conferences.
Talk to us. We aren’t always chasing a transaction.
Sources:
- ASD IRAP Consumer Guide, July 2025
- IRAP Common Assessment Framework, April 2025
- PSPF requirement 0086 and requirement 0109, Protective Security Policy Framework, 2024
- Cloud assessment and authorisation, cyber.gov.au, 2024
Last updated: 21 June, 2026